
Management · Software · Network

The RDA Blog

Practical guidance on the people, processes, and technology behind your organization’s work.

Organized by source edition month. RDA guidance reviewed October 21, 2026.

158 articles in the archive

Shared Logins Make It Hard to Know Who Still Has Access

Who Controls Your Organization’s Domain Name

A Password Reset May Leave Email Access Open

An Office Move Starts Before the Moving Truck

Keep Social Media Access Under Your Control

Your Software Vendor Reports a Breach

Separate permission to publish from approval of the message

Confirm site and carrier readiness before the move date

Test your way out of a cloud subscription

Replace computers when support and the work require it

Personal devices need an agreement before access

Guest Wi-Fi separation must be proved, not named

Give staff a way to get software without permanent admin rights

Build the IT budget around the work it must support

Your website needs an operating owner after launch

Search results are directions, not proof of identity

Put shared documents where the team can keep them

Make the monthly IT review a short list of decisions

Keep the work moving when Microsoft 365 is unavailable

Judge a suspicious message by the request

When a cyber incident starts, give the response a clear owner

Still running Windows 10? Check the edition and the update path

Protect your sending domain without breaking legitimate mail

Passkeys need a rollout plan, including recovery

Decide where the meeting record belongs before adding AI notes

A QR code deserves the same check as a link

Ransomware prevention needs several chances to stop an intrusion

Five tenant settings to review with the people who use them

Before Copilot, find out who can read the files

Ask what can delete your backup

Answer the insurance questionnaire from evidence

A clean departure starts with a properly created user

Verify the payment change through a trusted channel

Remove routine admin rights with a workable alternative

Move to passkeys without losing account recovery

Find the app access an account closure missed

Design safer work around everyday habits

A working MFA prompt can still be part of phishing

Test your data export before you need to leave

Protect the session after sign-in

Give the old server a documented future

Close the home workday without leaving records open

Check the recruiter before opening the assessment

A browser extension is an access decision

Turn zero trust into a sequence of changes

The app list finance, departments, and IT should share

Ransomware readiness needs an operating plan

Find out where AI enters the work

Check the handoffs between security tools

Agree the scope before discovering the apps in use

A work laptop needs a home working standard

Start zero trust with one important service

Put the workload where it fits

Give every cloud cost an owner

Check the access behind the vendor contract

Before an AI agent can act, decide who is responsible

An employee departure is an access and records handover

Working elsewhere needs a plan for the work

Move beyond codes with a recovery plan

Before renewing Copilot, ask what changed

A server refresh is a service decision

A familiar voice is not an approval

A cloud check needs a follow-up

Retire the data with the device

Guest Wi-Fi should have a small job

Contractor access needs an end date, not a reminder

Automate the cloud review before automating deletion

Approve the workflow before the SaaS trial

An AI upload is a data decision

Write an AI policy people can use

Test the task, not just the page

Safer online purchases still need an approval process

Read the permissions before clicking Connect

Make the privacy notice match the work

Give purchasing accounts an owner and a spending boundary

A license review starts with the role

Protect the account, not only the password

Give AI a defined job before giving it your data

Cloud compliance still needs an owner

Before you send that form

An IT plan that survives Monday morning

A discount is not a device plan

Work out which data rules apply before writing the policy

Turn the technology wish list into an authorized sequence

Treat repeated IT friction as a service problem

Strengthen the whole account, not just its password

Make a report answer one operational question

Buy an AI capability for a defined job

Write the procedure for the colleague covering tomorrow

Publish a procedure someone else can follow

Plan IT spending in the month the work happens

Give the project an owner before creating its task board

Fix the meaning of the data before cleaning the rows

Find the Wi-Fi problem before buying more access points

Bring connected office equipment into the support plan

Review suppliers by what they can reach

Read the cloud invoice alongside the workload

Make the first login the end of a prepared handover

Give each record a reason to stay and a rule for leaving

Build a Power Automate flow someone else can support

A refresh plan starts before the next computer fails

Take a service map to the cyber insurance conversation

Start a backup plan with the work you need back

Roll out MFA without leaving recovery to chance

Remote security begins with an approved way to work

Choose cloud storage by the files and the people using them

Automate one small handoff before asking AI to do more

Review every route into an account

One common password, many accounts

Follow the information through the website

Cloud storage security is an operating arrangement

An exposure alert needs a response

A password policy must support real sign-in

Make the desktop fit the task

Make one Microsoft 365 workflow work well

Look for behavior as well as bad files

Deleted is not one state

Choose cloud storage around the records

Check the whole Google account

Size storage for the work and its recovery

Replace a device for a defined reason

Read beyond the Cyber Trust Mark

Ransomware is one kind of malware

Give mobile apps only the work they need

Check ownership and license rights before buying used IT

Buy the supported life of used equipment

The work around an AI answer

Secure file sharing begins with the recipient

Report the symptom before trying a cure

Reduce exposure at each data handoff

Limit ransomware disruption before recovery begins

A tidier device starts with clear records

Protect the copies and the way back

Look at the path from request to intrusion

Follow the exposure after a vault incident

Encrypted where, and who can recover it?

Classify information before choosing its handling rules

Buy the task, not an AI collection

Ask what a shared ledger would solve

Agree the rules before sharing a ledger

Turn exposure findings into finished work

The camera needs an owner too

Make everyday security a supported routine

Keep smart-home convenience out of work access

Give the password vault an organizational home

A leaked-account alert starts a check

Set up Windows around the actual desk

Read the breach notice before choosing a response

Make the approved download easy to find

Collect logs someone can use

Ask where AI already enters the work

Add payment options and keep a workable fallback

Keep the record's purpose with its copies

Follow one request before replacing the service tools

Email protection needs more than a mailbox setting

Choose AI by the handoff it improves

A rushed cleanup can hide the breach

A meeting summary needs a record owner

RDA VISUAL GUIDE

Find the guidance behind the next decision

Use a topic and service area to follow the people, processes and technical dependencies.
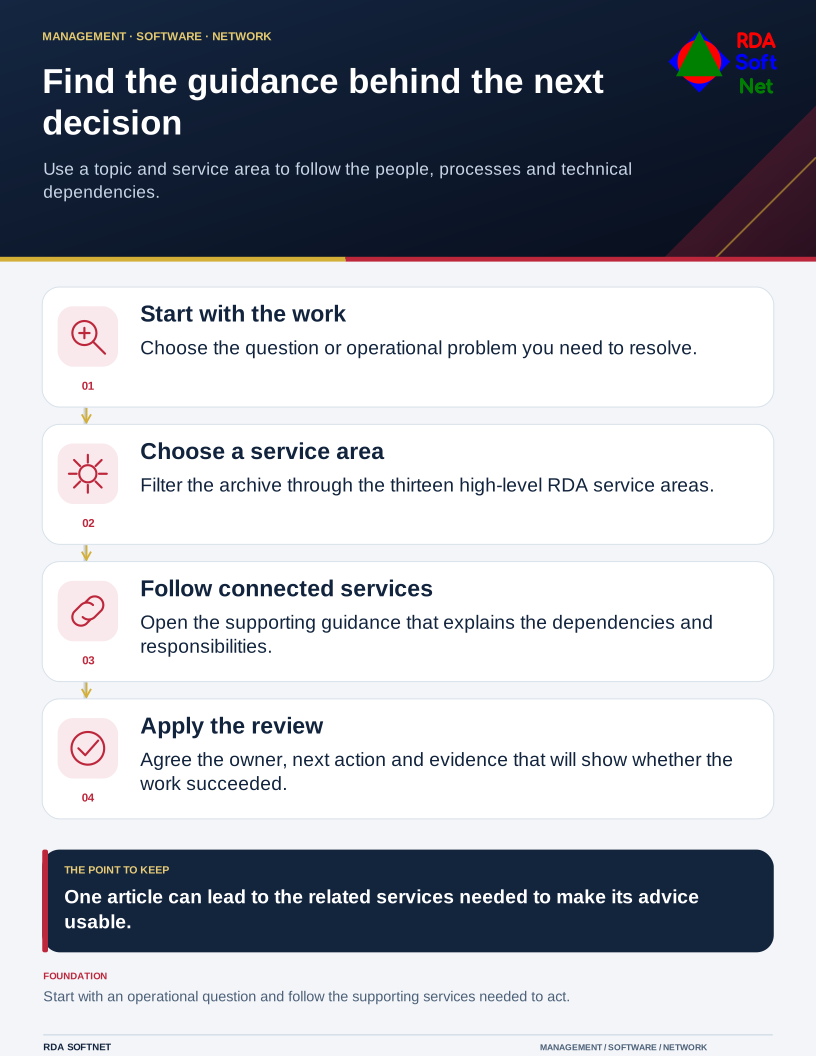
Find the guidance behind the next decision. Use a topic and service area to follow the people, processes and technical dependencies.