
A member of staff spots an unfamiliar message in Sent Items and changes their password. Later, more messages appear. The reset was a reasonable first action, but the account may have other routes through which access continues.
Review the access behind the mailbox
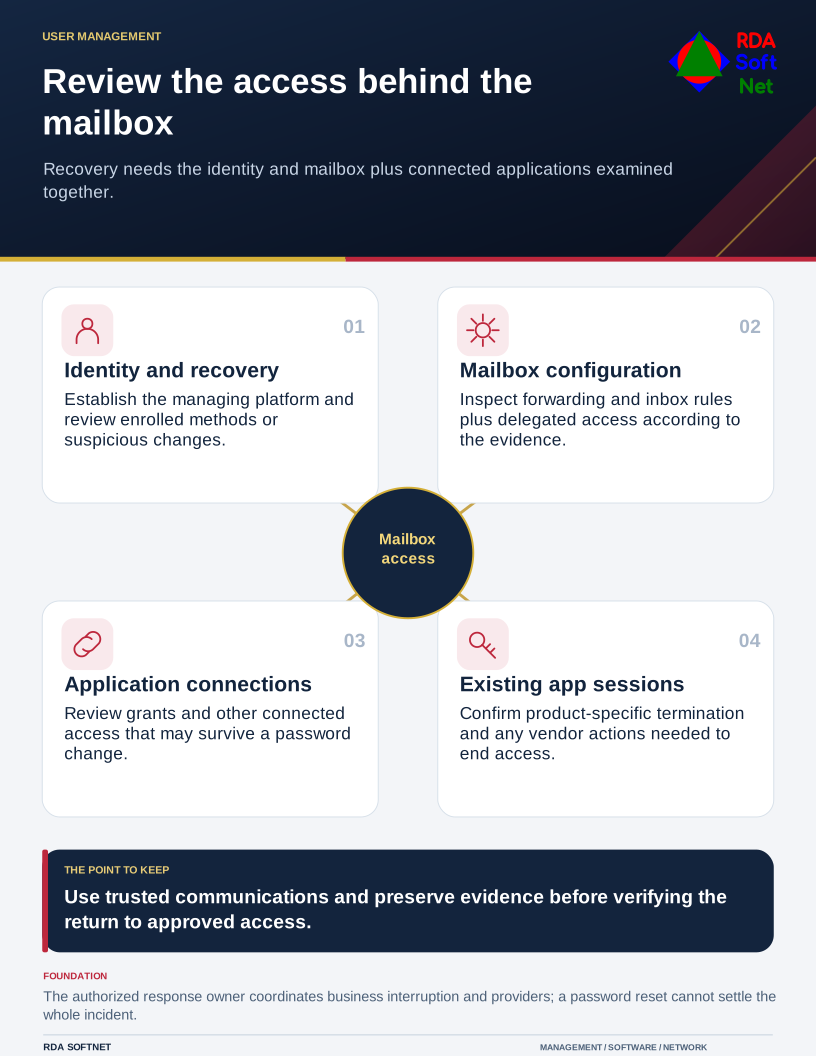
Recovery needs the identity and mailbox plus connected applications examined together.
An email compromise needs a coordinated incident response. RDA looks at the identity, mailbox, connected applications, and available activity records together so the response does not stop at one changed setting.
Establish the identity and affected systems
Identify where the account is managed and which services depend on it. In Microsoft 365, that can include the cloud identity as well as the mailbox and other connected resources. Preserve the information needed to investigate while the authorized response team contains access.
Check more than the password
Microsoft's response guidance includes account protection and review of suspicious mailbox activity. Forwarding and inbox rules, authentication methods, application permissions, and active access all deserve attention based on the evidence. Microsoft compromised account guidance
The identity service and application may manage sessions differently. Some applications issue their own session tokens, so a central account change does not instantly end every application session. See how access removal fits the user lifecycle.
Coordinate containment and business continuity
The response owner should identify who may disable the account, what legitimate work will be affected, and which vendor actions are required. Use a trusted communication channel if the normal mailbox may be compromised. Keep a record of actions and significant findings.
Verify recovery before closing the work
Restore approved access, confirm the intended authentication and recovery methods, and review whether forwarding, delegated access, or application connections still create unwanted access. Continue the monitoring appropriate to the incident and the available records. Read about Credential Security and MFA.
Management, legal, privacy, insurance, or regulatory responsibilities may also be triggered by what the investigation establishes. Those decisions need the responsible people and actual incident facts; a password reset cannot settle them.
RDA can coordinate technical containment, application owners, and the handoffs needed for recovery. The work is complete when the intended access is restored and the findings and remaining actions are documented.