
Identify where the user account is created
User Credentials begins with an established identity source. In a Windows domain, Active Directory Domain Services stores directory information, and domain controllers provide the directory and authentication functions. Other environments may use a different directory or a cloud identity platform. LDAP is a protocol used to access directory services, rather than the name of a complete account management platform.
Find the account's authoritative home
User creation depends on an understood path through identity and supporting services.
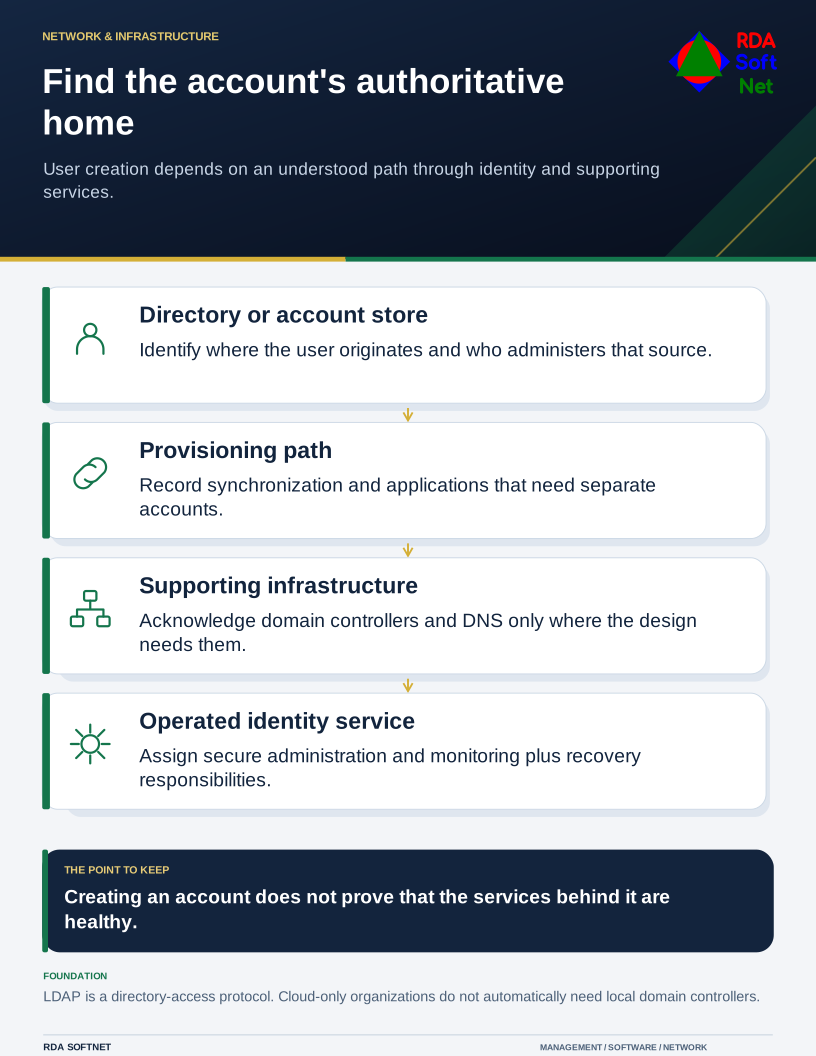
Microsoft Entra ID can provide cloud identity management. Some applications also maintain their own user directory. The account creation process must identify the correct source for each system and any synchronization or separate provisioning that is required. Microsoft directory service comparison
Connect account management with its supporting services
User Management depends on the infrastructure and cloud services that support the account. Network and Infrastructure, Cloud-Based Applications, and Hybrid Cloud may all contribute to the identity environment. Establish which services are involved and who is responsible for each.
These are connected service responsibilities. Creating an account does not by itself establish that the directory, synchronization, or dependent application is healthy.
Dependencies to acknowledge
- The directory or cloud identity service and its accountable administrator.
- Domain controller availability and supporting DNS where the design requires them.
- Synchronization and provisioning connections in a hybrid environment.
- Secure administrative access, monitoring, and recovery arrangements.
- The target application's ability to use the identity or require a separate account.
The specific architecture is established during discovery. A cloud-only organization does not automatically need an on-premises domain controller. RDA documents which services support user creation and who is responsible for each one.
Return to User Credentials to see how provisioning, security, staff changes, and auditing fit around that foundation.