
Begin with an authorized departure instruction
The responsible manager or designated authority supplies the person's identity, affected role, effective time, and any restrictions on communication. Use a trusted approval channel and an account inventory so IT is not guessing which systems the person uses.
End the access and preserve the work
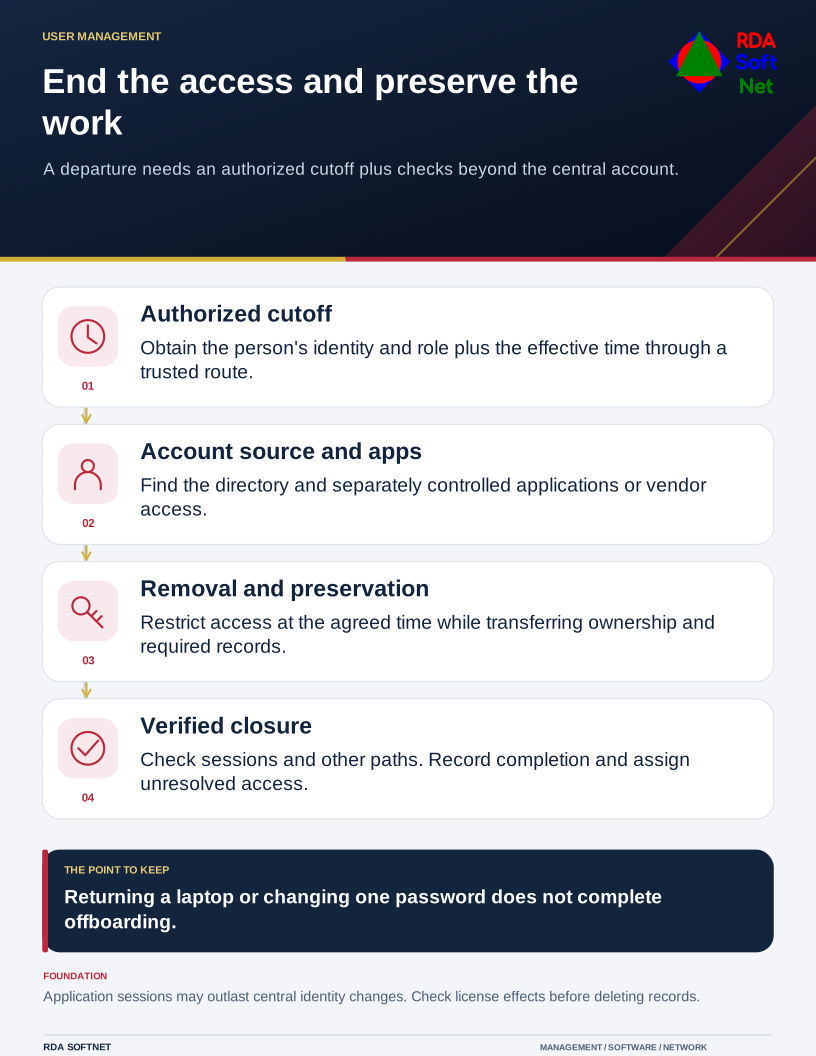
A departure needs an authorized cutoff plus checks beyond the central account.
Remove access at its source and in connected services
Identify the directory or identity platform that controls the account. Disable the relevant identity, revoke supported sessions, and remove direct accounts or delegated access in applications that require separate action. Microsoft explains that an application can retain its own session token; central identity changes alone may not end every application session immediately. Microsoft access revocation guidance
Check VPN access, shared mailboxes, vendor portals, authenticator methods, recovery contacts, and shared credentials known to the departing person. A returned laptop is one part of offboarding, not a complete account closure.
Coordinate records and continuity
Access removal and data preservation are separate tasks. Disable access promptly at the authorized time while arranging required retention, ownership transfer, mailbox handling, and legal holds. Confirm the consequences of deleting an account or removing a license before taking those actions. Keep business processes and service accounts from depending on a departed person's identity.
Record completion and exceptions
The work record should identify the instruction, systems checked, completion times, and unresolved dependencies. Application owners or vendors confirm actions outside IT's direct control. Escalate a remaining access path to its owner and record the follow-up.
The dependencies are the identity source, reliable management notification, account inventory, vendor cooperation, retention decisions, and the authority to make the changes. RDA coordinates those pieces through the user management workflow rather than treating a password change as completion.