
Begin with the identity source
Identify the directory or platform where each user is created. Record whether access is controlled by AD DS and domain controllers, another directory, a cloud identity service, or the individual application. In hybrid systems, acknowledge synchronization and any accounts that need separate provisioning.
Turn a credential discussion into owned work
The checklist starts with identity and ends with verified actions rather than a compliance score.
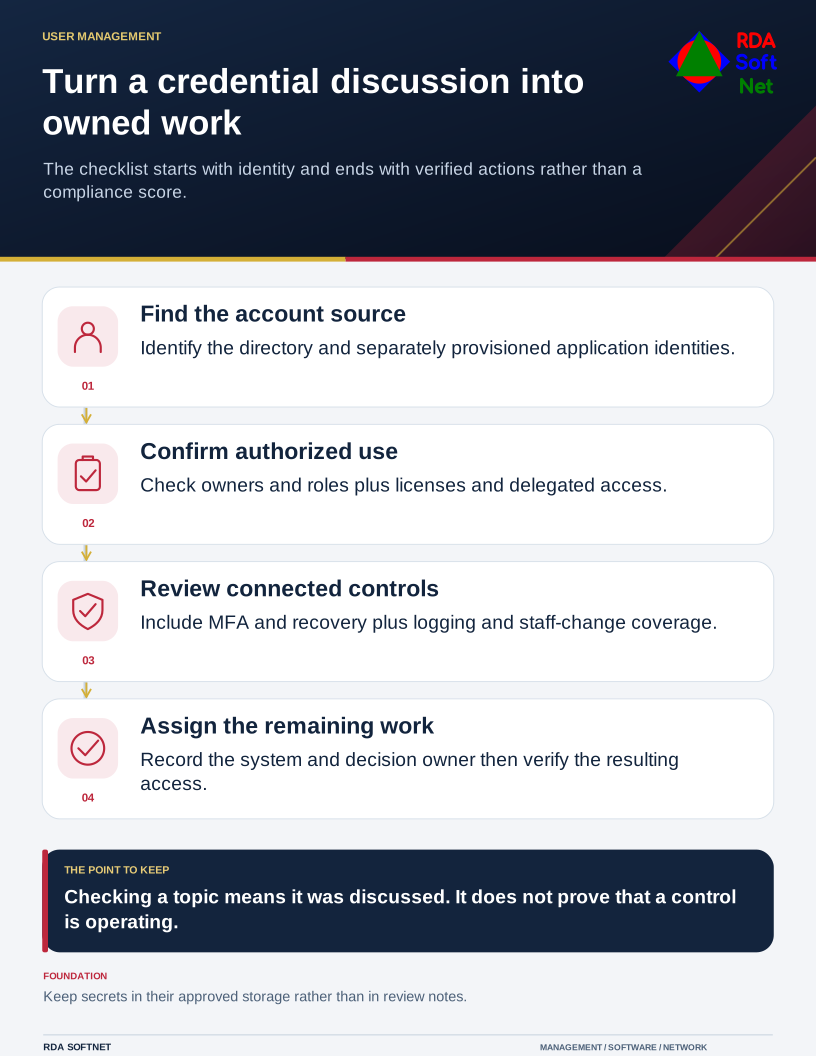
Review the connected responsibilities
Use the checklist below to structure a review with your manager, IT staff, and application owners. A checked item means that it has been discussed; it is not a compliance rating or a claim that a control has been implemented.
Topics to review
Turn findings into assigned work
Record the account or system, the responsible owner, the decision needed, and who will complete the action. Keep passwords, recovery codes, and other secrets out of the review notes. Use the approved work-record and credential-storage systems for their respective purposes.
RDA can use the resulting list to coordinate account changes, vendor involvement, and follow-up. Dependencies are acknowledged at the service level; the technical design and task instructions are developed for the specific environment.