
Management · Management Operations
Security monitoring and escalation
Security-event monitoring, collected log sources and the handoff between the monitoring provider and RDA.
Features and benefits
| Feature | Practical benefit |
|---|---|
| Endpoint, network and cloud event collection | Supported sources can be brought into one monitoring workflow, reducing separate queues and missed handoffs. |
| Analyst triage and threat hunting | Analyst review and threat intelligence help distinguish suspicious activity from routine events under the contracted monitoring scope. |
| Detection beyond antivirus alerts | Collected logs and behavioral indicators can expose suspicious activity that a single prevention tool does not explain. |
| Escalation and service-ticket integration | Incident handoffs give RDA an actionable starting point and a record of who owns the response. |
| Source and incident reporting | Event, device and incident records support investigation, monitoring-coverage checks and response follow-up. |
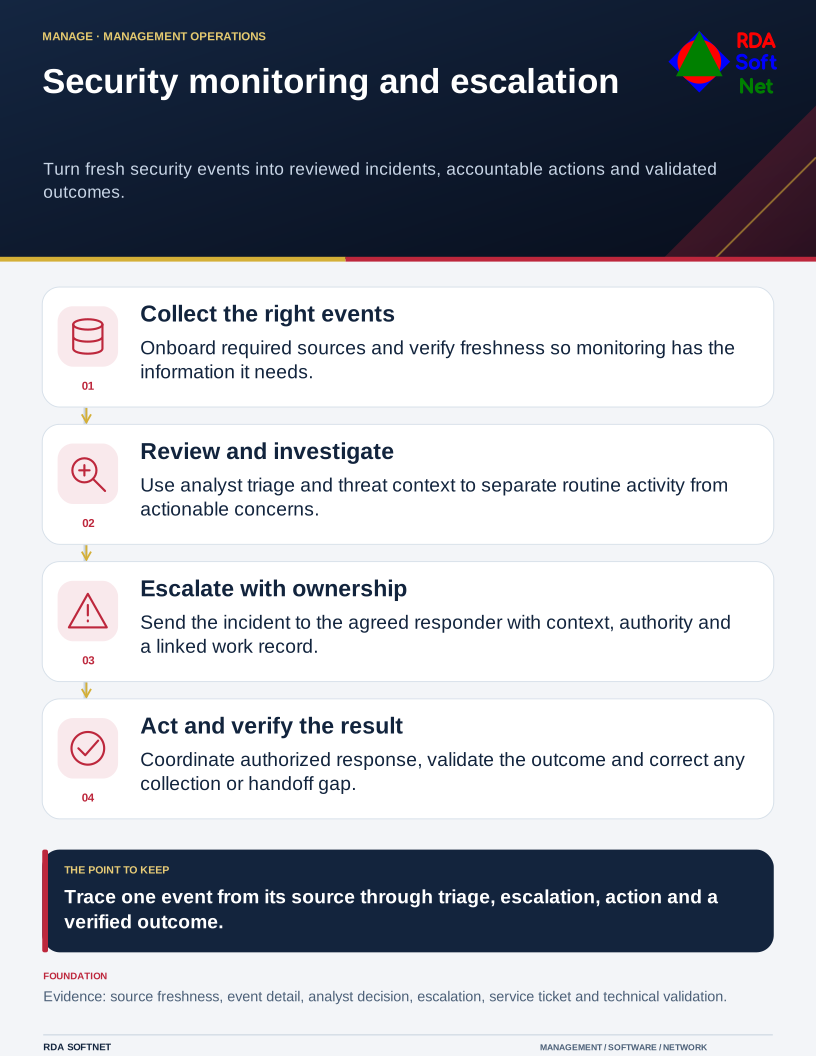
Security monitoring and escalation
Turn fresh security events into reviewed incidents, accountable actions and validated outcomes.
Requirements → deployment → operation → validation
Document library
Requirements and security baseline
Security monitoring and escalation Requirements and security baseline
Baseline alignment. Logging, detection and response safeguards selected for the agreed CIS IG. CIS IGs
- In-scope devices, applications and log sources
- Collection settings, suppression rules and telemetry retention
- Provider, RDA and client response responsibilities
Deployment and control mapping
Security monitoring and escalation Deployment and control mapping
- Scope and ownership: Security-event monitoring, collected log sources and the handoff between the monitoring provider and RDA.
- Approved rollout and acceptance: Pilot onboarding and initial event receipt; representative event-to-escalation acceptance test
- Applicable requirements mapped to configuration, validation evidence and approved exceptions
Client and user guide
Security monitoring and escalation Client and user guide
- How to report suspicious activity and suspected incidents
- What an escalation may require from the client
- Approved communication and incident contact routes
Technician training outline
Security monitoring and escalation Technician training outline
- Source onboarding, telemetry health and event interpretation
- Incident triage, suppression review and escalation handling
- Evidence collection, ticket updates and closure validation
RDA technician workflow
Security monitoring and escalation RDA technician workflow
- Identify and assess the requirement; plan the scope, accountable owner and required approvals
- Implement and verify: Trace a representative event from its source through triage, escalation, RDA action and a documented outcome.
- Document the configuration and result; hand off operation, review exceptions and plan lifecycle changes
Portal and access training
Security monitoring and escalation Portal and access training
- Client boundaries and named operator access
- Multifactor authentication and least-privilege roles
- Integration credentials, access review and offboarding
Training module template
Security monitoring and escalation Training module template
- Learning objectives and prerequisites: source onboarding, telemetry health and event interpretation
- Authorized practical exercise: Trace a representative event from its source through triage, escalation, RDA action and a documented outcome.
- Knowledge check, observed result and instructor or responsible-owner sign-off
Basic installation and acceptance
Security monitoring and escalation Basic installation and acceptance
- Approved agent or source prerequisites
- Pilot onboarding and initial event receipt
- Representative event-to-escalation acceptance test
Advanced deployment and changes
Security monitoring and escalation Advanced deployment and changes
- Additional supported data sources and collection tuning
- Controlled suppression changes with documented justification
- Staged collector or agent updates and rollback
Technical configuration and integrations
Security monitoring and escalation Technical configuration and integrations
- Onboarded endpoint, network and cloud sources with timestamp and freshness checks
- Provider response scope, escalation authority and approved service-ticket integration
- Suppression, export, retention and collection-health settings
Operational audit and checklist
Security monitoring and escalation Operational audit and checklist
- Coverage and operating checks: missing or stale telemetry from required sources
- Evidence sample: dated device, event and incident exports supported by the portal; soc escalation, rda action and validated ticket closure
- Review date and owner; pass or fail, exceptions, corrective action and retest evidence
Tabletop exercises
Security monitoring and escalation Tabletop exercises
- A required source stops sending events
- A high-priority escalation arrives outside normal staffing
- A suppression rule hides a meaningful event
Response playbook
Security monitoring and escalation Response playbook
- Assess event credibility, affected scope and business impact
- Coordinate provider and RDA actions with explicit authority
- Validate recovery and resolve monitoring or escalation gaps
Operational runbooks
Security monitoring and escalation Operational runbooks
- Restore event collection from an onboarded source
- Acknowledge and work a SOC escalation
- Export incident evidence and validate case closure
Evaluation and lifecycle review
Security monitoring and escalation Evaluation and lifecycle review
Selection and fit. Compare viable options against the business need, security requirements, existing systems and full operating cost. Record the reasons for the selection, the tradeoffs accepted and the conditions that would prompt a different choice.
Keeping the choice current. Follow supplier notices between scheduled reviews and reassess before renewal or a material change. Check ownership changes, renamed or retired products, subscription and licensing terms, pricing, capabilities and support commitments. Record the effect on security, data handling, integrations and service continuity. Assign an owner to approve adjustments or plan a transition, including data export and removal of access.
- Required source coverage and actual escalation performance
- Provider responsibilities, entitlements and retention
- Integration reliability, noise and total operating effort