
Management · Management Operations
Governance, risk and control evidence
Control assessments, responsibility tracking and organized evidence for the agreed governance scope.
Features and benefits
| Feature | Practical benefit |
|---|---|
| Requirements and control mapping | Organizes selected frameworks and links requirements to implementation records so responsibility and gaps are easier to understand. |
| Evidence requests and refresh cycles | Assigned requests and current artifacts reduce repeated evidence chasing while retaining assessment history. |
| Policies, procedures and ownership | Governance records connect expectations to the people responsible for maintaining and approving them. |
| Risk register and treatment actions | Impact and risk scoring help prioritize mitigation, accepted risks and the work needed to reach a target state. |
| Assessment and evidence reporting | Progress views and scoped exports help prepare an assessment package; completion scores alone do not establish effective controls. |
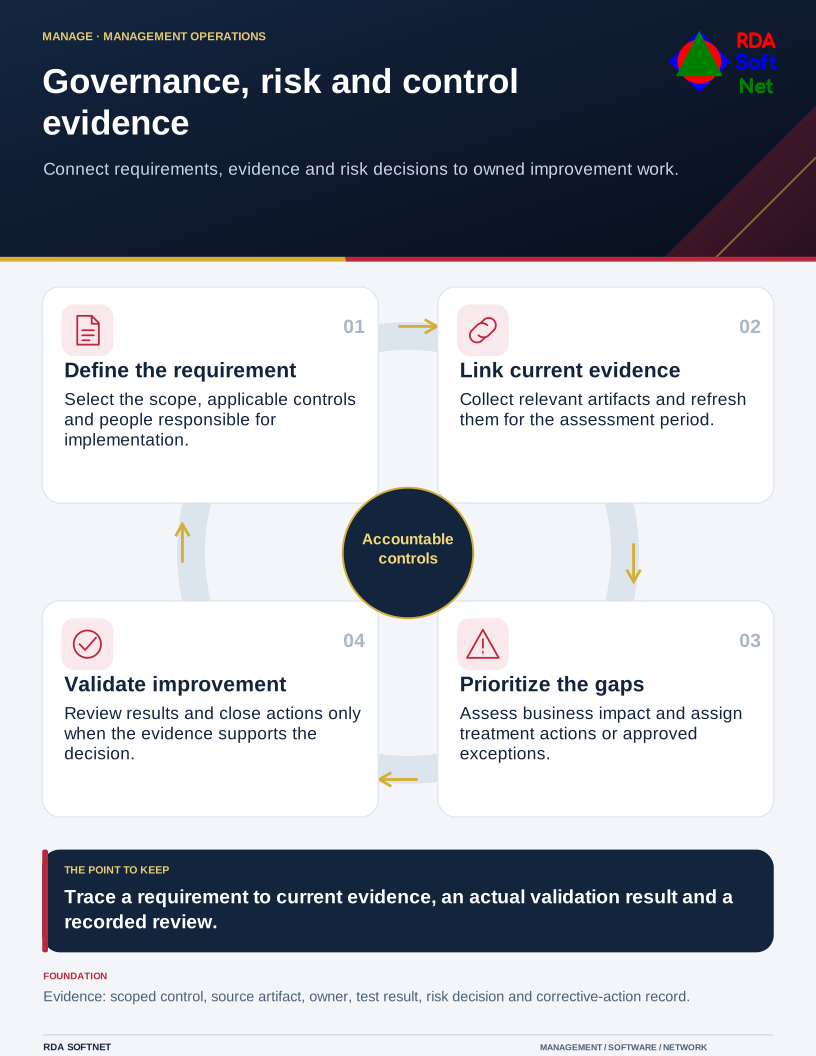
Governance, risk and control evidence
Connect requirements, evidence and risk decisions to owned improvement work.
Requirements → deployment → operation → validation
Document library
Requirements and security baseline
Governance, risk and control evidence Requirements and security baseline
Baseline alignment. Agreed control scope, baseline revisions, assessment evidence and approved exceptions. CIS IGs · DISA STIGs · DISA SRGs
- Assessment scope, selected framework and control owners
- Evidence quality, policy ownership, review dates and applicability decisions
- Risk scoring, treatment actions, accepted risk and reviewer responsibilities
Deployment and control mapping
Governance, risk and control evidence Deployment and control mapping
- Scope and ownership: Control assessments, responsibility tracking and organized evidence for the agreed governance scope.
- Approved rollout and acceptance: Pilot controls, accountable owners and evidence requests; sample control-to-artifact trace and reviewer acceptance
- Applicable requirements mapped to configuration, validation evidence and approved exceptions
Client and user guide
Governance, risk and control evidence Client and user guide
- Control-owner responsibilities and evidence requests
- Submitting current artifacts and explaining exceptions
- Review decisions, follow-up actions and status communication
Technician training outline
Governance, risk and control evidence Technician training outline
- Assessment setup and control-to-evidence relationships
- Evidence currency, test results and applicability review
- Reporting gaps and maintaining an action register
RDA technician workflow
Governance, risk and control evidence RDA technician workflow
- Identify and assess the requirement; plan the scope, accountable owner and required approvals
- Implement and verify: Sample a control from stated requirement through a current artifact, actual validation result, owner and recorded review decision.
- Document the configuration and result; hand off operation, review exceptions and plan lifecycle changes
Portal and access training
Governance, risk and control evidence Portal and access training
- Organization boundaries and least-privilege roles
- Evidence access and reviewer permissions
- Account lifecycle, access review and export permissions
Training module template
Governance, risk and control evidence Training module template
- Learning objectives and prerequisites: assessment setup and control-to-evidence relationships
- Authorized practical exercise: Sample a control from stated requirement through a current artifact, actual validation result, owner and recorded review decision.
- Knowledge check, observed result and instructor or responsible-owner sign-off
Basic installation and acceptance
Governance, risk and control evidence Basic installation and acceptance
- Approved assessment scope and framework selection
- Pilot controls, accountable owners and evidence requests
- Sample control-to-artifact trace and reviewer acceptance
Advanced deployment and changes
Governance, risk and control evidence Advanced deployment and changes
- Additional scoped controls and reusable evidence relationships
- Risk and exception workflows with approval records
- Report configuration and assessment-cycle changes
Technical configuration and integrations
Governance, risk and control evidence Technical configuration and integrations
- Artifact storage references and evidence ownership
- Approved imports, exports and integration boundaries
- Retention, review history and access controls
Operational audit and checklist
Governance, risk and control evidence Operational audit and checklist
- Coverage and operating checks: missing, stale or incomplete evidence
- Evidence sample: assessment status and control-to-evidence relationships; gap register, assigned actions and closure or risk-acceptance records
- Review date and owner; pass or fail, exceptions, corrective action and retest evidence
Tabletop exercises
Governance, risk and control evidence Tabletop exercises
- A control is marked complete but its artifact is stale
- A reviewer challenges an accepted-risk decision
- An assessment must be handed to a different owner
Response playbook
Governance, risk and control evidence Response playbook
- Assess evidence quality and the actual control gap
- Assign corrective work or an authorized exception
- Validate the new result and record the reviewer decision
Operational runbooks
Governance, risk and control evidence Operational runbooks
- Create an evidence request and assign its owner
- Review an artifact and record limitations
- Export scoped assessment evidence and update the action register
Evaluation and lifecycle review
Governance, risk and control evidence Evaluation and lifecycle review
Selection and fit. Compare viable options against the business need, security requirements, existing systems and full operating cost. Record the reasons for the selection, the tradeoffs accepted and the conditions that would prompt a different choice.
Keeping the choice current. Follow supplier notices between scheduled reviews and reassess before renewal or a material change. Check ownership changes, renamed or retired products, subscription and licensing terms, pricing, capabilities and support commitments. Record the effect on security, data handling, integrations and service continuity. Assign an owner to approve adjustments or plan a transition, including data export and removal of access.
- Traceability and evidence quality across sampled controls
- Assessment scope, framework maintenance and reporting
- Access protection, review effort and total cost