
Management · Management Operations
Endpoint protection and response
Endpoint protection, threat investigation and response for the devices in the agreed service scope.
Features and benefits
| Feature | Practical benefit |
|---|---|
| Malware and ransomware prevention | Behavior-based and file-based detection helps stop malicious activity, including attacks that do not rely on a traditional executable. |
| Endpoint investigation | Searchable endpoint activity and attack timelines help trace how a threat started and which devices need attention. |
| Containment and remediation | Authorized isolation and remediation limit spread; rollback on supported systems can assist recovery from unwanted changes. |
| Device and host firewall controls | Policies for removable devices and host network access reduce exposure where supported and configured. |
| Central policy and agent visibility | A shared view of protection status, exclusions and disconnected devices makes coverage gaps easier to find. |
| Response records and integrations | Recorded threat actions and approved integrations connect a detection to an accountable investigation and service ticket. |
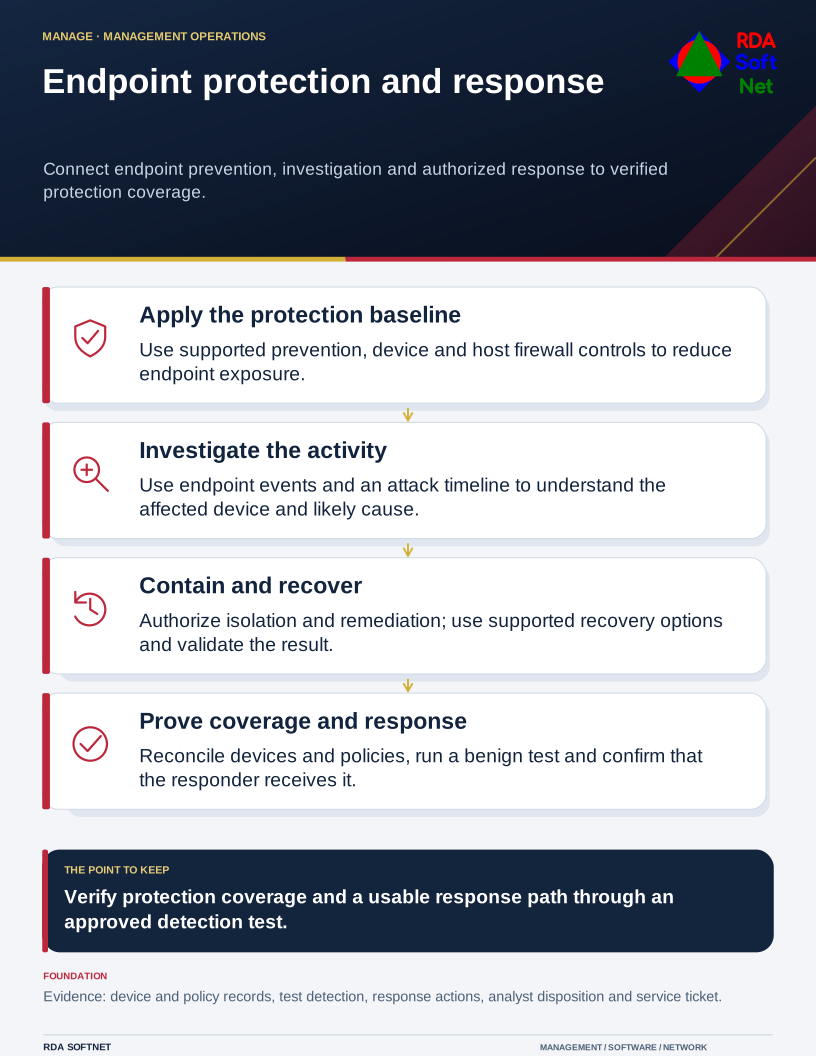
Endpoint protection and response
Connect endpoint prevention, investigation and authorized response to verified protection coverage.
Requirements → deployment → operation → validation
Document library
Requirements and security baseline
Endpoint protection and response Requirements and security baseline
Baseline alignment. Malware protection and response safeguards selected for the agreed CIS IG. CIS IGs
- Supported endpoints, service boundaries and accountable owners
- Prevention, tamper protection, device and host firewall policies with approved exclusions
- Threat severity, containment authority, recovery limits and evidence retention
Deployment and control mapping
Endpoint protection and response Deployment and control mapping
- Scope and ownership: Endpoint protection, threat investigation and response for the devices in the agreed service scope.
- Approved rollout and acceptance: Pilot installation and correct site or group enrollment; agent connectivity, effective policy and installation acceptance
- Applicable requirements mapped to configuration, validation evidence and approved exceptions
Client and user guide
Endpoint protection and response Client and user guide
- What the endpoint protection agent does and what users may notice
- Reporting suspicious activity and requesting support
- User responsibilities and limits of endpoint protection
Technician training outline
Endpoint protection and response Technician training outline
- Console navigation, site structure and protection coverage
- Attack investigation, device controls, host firewall policy and false positives
- Authorized containment, supported remediation and recovery validation
RDA technician workflow
Endpoint protection and response RDA technician workflow
- Identify and assess the requirement; plan the scope, accountable owner and required approvals
- Implement and verify: Reconcile endpoint coverage, run an approved benign detection test, verify the response handoff and sample the configured device or host firewall policy.
- Document the configuration and result; hand off operation, review exceptions and plan lifecycle changes
Portal and access training
Endpoint protection and response Portal and access training
- Named users, least privilege and multifactor authentication
- Site boundaries, role assignment and access review
- Service accounts, API tokens and access removal
Training module template
Endpoint protection and response Training module template
- Learning objectives and prerequisites: console navigation, site structure and protection coverage
- Authorized practical exercise: Reconcile endpoint coverage, run an approved benign detection test, verify the response handoff and sample the configured device or host firewall policy.
- Knowledge check, observed result and instructor or responsible-owner sign-off
Basic installation and acceptance
Endpoint protection and response Basic installation and acceptance
- Endpoint prerequisites and approved installation package
- Pilot installation and correct site or group enrollment
- Agent connectivity, effective policy and installation acceptance
Advanced deployment and changes
Endpoint protection and response Advanced deployment and changes
- endpoint management rollout and deployment exception handling
- Staged upgrades, policy changes and approved exclusions
- VDI or other special workloads where supported and licensed
Technical configuration and integrations
Endpoint protection and response Technical configuration and integrations
- Site configuration, policy inheritance and endpoint inventory
- Approved API, webhook or monitoring integration
- Telemetry scope, collection health and retention settings
Operational audit and checklist
Endpoint protection and response Operational audit and checklist
- Coverage and operating checks: offline or unhealthy agents and protection-policy drift
- Evidence sample: endpoint inventory, last contact and effective policy records; approved detection test, analyst disposition and linked service ticket
- Review date and owner; pass or fail, exceptions, corrective action and retest evidence
Tabletop exercises
Endpoint protection and response Tabletop exercises
- Ransomware affecting several devices or sites
- An offline agent during a suspected compromise
- A false positive disrupting an essential application
Response playbook
Endpoint protection and response Response playbook
- Detection and analysis using threat context and business impact
- Containment authority, escalation and evidence preservation
- Eradication, recovery checks and lessons returned to the baseline
Operational runbooks
Endpoint protection and response Operational runbooks
- Agent offline recovery and supported agent upgrade
- Threat triage, authorized isolation and false-positive handling
- Endpoint recovery verification and decommissioning
Evaluation and lifecycle review
Endpoint protection and response Evaluation and lifecycle review
Selection and fit. Compare viable options against the business need, security requirements, existing systems and full operating cost. Record the reasons for the selection, the tradeoffs accepted and the conditions that would prompt a different choice.
Keeping the choice current. Follow supplier notices between scheduled reviews and reassess before renewal or a material change. Check ownership changes, renamed or retired products, subscription and licensing terms, pricing, capabilities and support commitments. Record the effect on security, data handling, integrations and service continuity. Assign an owner to approve adjustments or plan a transition, including data export and removal of access.
- Detection and response performance against agreed test cases
- Supported workloads, licensing and operational effort
- Integration, scalability, training and total cost of ownership