
Establish applicability first
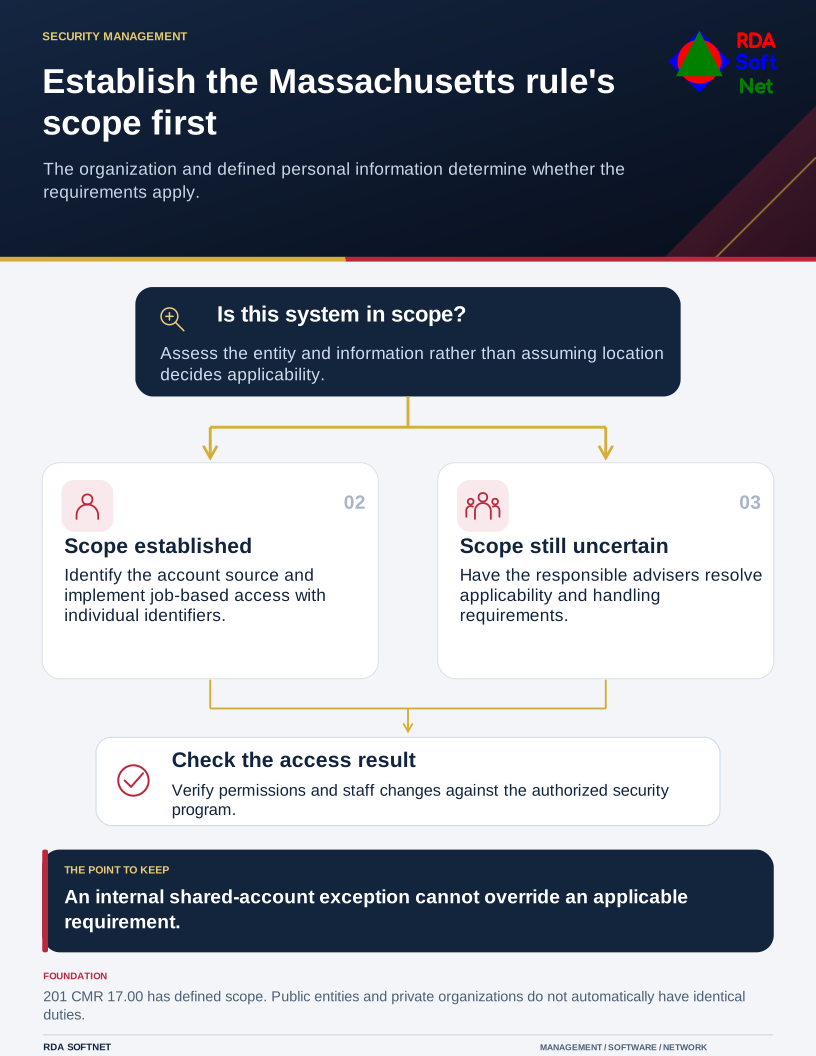
Massachusetts' 201 CMR 17.00 addresses the protection of defined personal information about Massachusetts residents. The regulation's definitions and scope matter; being located in Massachusetts is not by itself a complete applicability assessment. Do not assume every public entity and private organization has identical obligations under this regulation.
Establish the Massachusetts rule's scope first
The organization and defined personal information determine whether the requirements apply.
Connect user credentials to access control
For organizations and computer systems within scope, 17.04 addresses access based on job need and individual identifiers with non-default passwords. Massachusetts data security regulation
Review how the directory or application creates users, which roles expose personal information, and how access is removed. A common staff login can make it difficult to apply individual permissions and trace activity. Evaluate remaining shared accounts against the actual requirement rather than assuming an internal exception resolves it.
Acknowledge the dependencies
The information inventory, responsible organizational owner, identity source, application capabilities, authentication settings, and staff-change process support the access decision. Keep those responsibilities aligned with the organization's written information security program where required.
RDA can help document the systems and controls involved and coordinate the technical work with the organization's responsible advisers and management.