
Apply the governing agency requirements
The FBI CJIS Security Policy version 6.1, dated June 25, 2026, includes unique identification and authentication of organizational users in IA-2. Account management in AC-2 addresses authorization, account reviews, staff changes, and changing shared or group authenticators when individuals are removed. IA-5 also addresses changes to group or role authenticators. FBI CJIS Security Policy
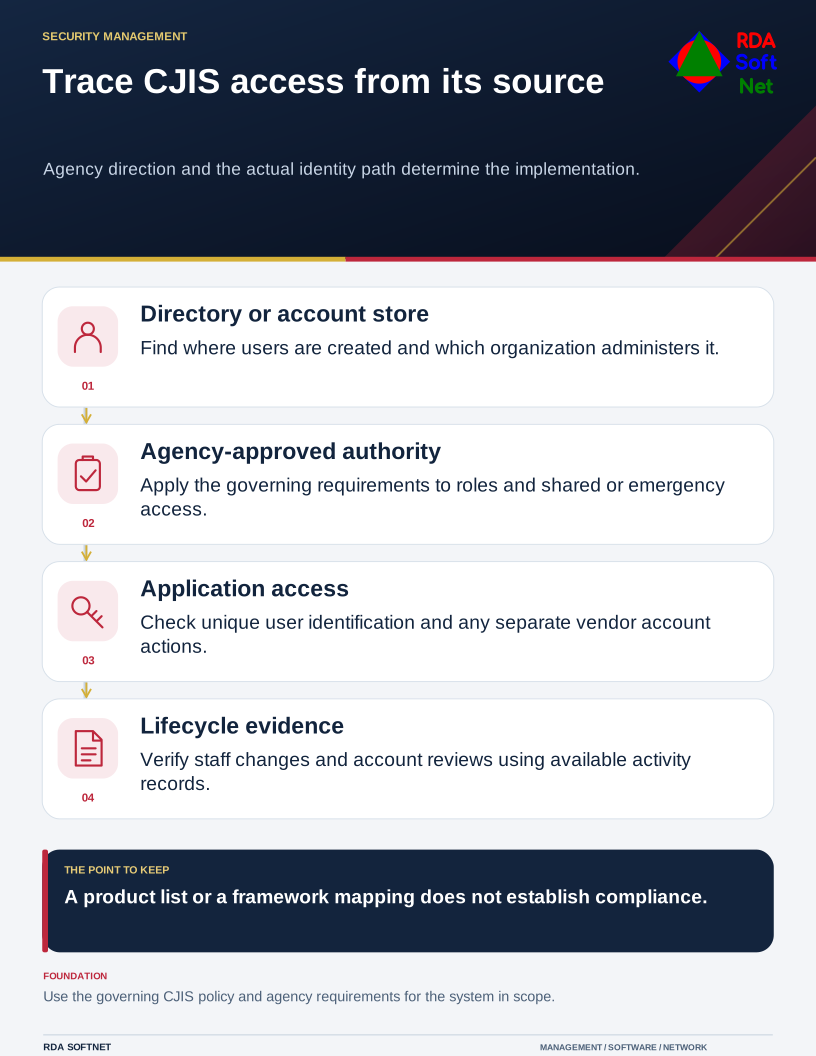
Trace CJIS access from its source
Agency direction and the actual identity path determine the implementation.
Check how an identity reaches the application
Identify the directory, domain controller, cloud identity service, or application account store that supports the access. Establish which organization controls each part of the path and how a departure or role change reaches it. A vendor-managed application may require a separate administrative action.
Acknowledge the operational dependencies
Agency approval, account ownership, appropriate authentication, secure administrative access, activity records, and the approved user lifecycle procedure are connected controls. Shared or emergency access must be evaluated against the actual policy and agency requirements, rather than assuming a general password-sharing exception applies.
RDA can coordinate the service responsibilities with the agency and the applicable CJIS authority. The configuration, agency direction, and evidence determine the implementation; a list of products or a framework mapping does not establish compliance.