
Network · Network & Infrastructure
Site-to-site and remote-access VPN
Site-to-site and remote-access VPN services, with the gateway, client and access requirements documented for each deployment.
Features and benefits
| Feature | Practical benefit |
|---|---|
| Encrypted network tunnels | Supported tunnel protocols protect traffic between approved endpoints or sites over an untrusted network. |
| Site-to-site connectivity | Defined routes and selectors connect required services between locations without exposing the whole internal network. |
| Remote-user access | An approved client or supported access method connects authorized people to the services they need away from the office. |
| Authentication and restricted routes | Configured identity checks, multifactor authentication and access policies limit entry to the intended users and destinations. |
| Session and tunnel diagnostics | Connection and traffic records help distinguish authentication, routing and application problems and verify access removal. |
Site-to-site and remote-access VPN
Provide authorized connectivity while limiting the people, routes and services a tunnel can reach.
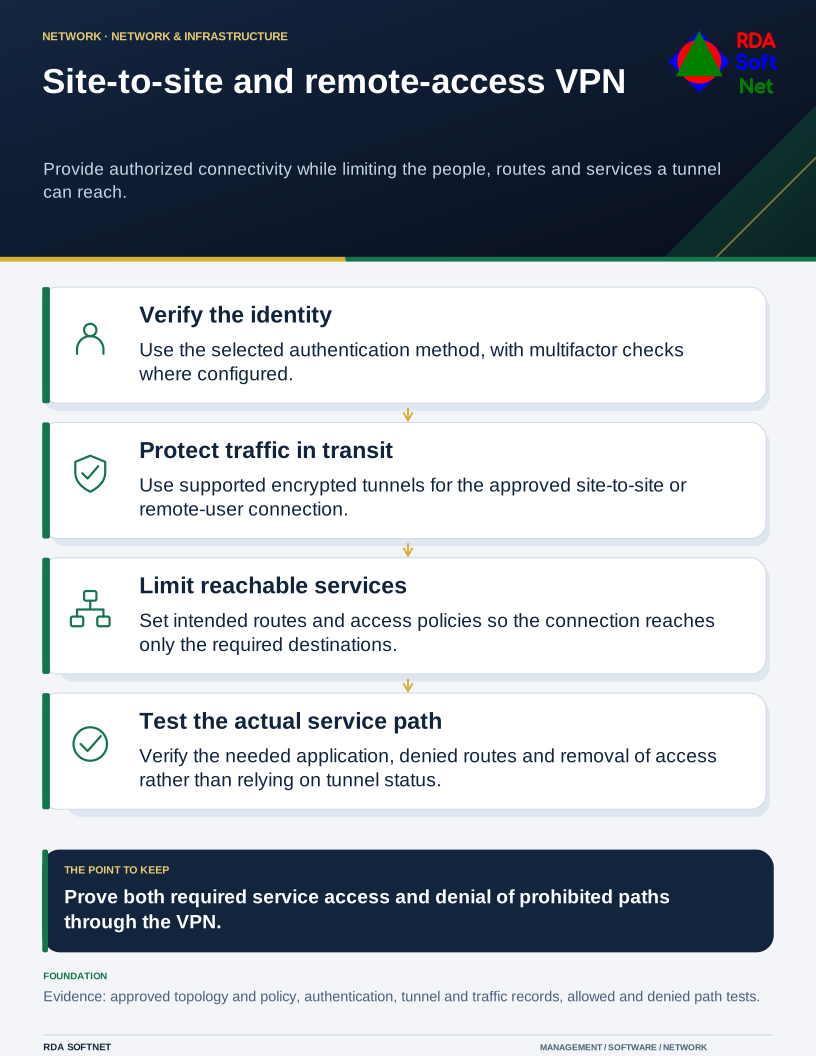
Requirements → deployment → operation → validation
Document library
Requirements and security baseline
Site-to-site and remote-access VPN Requirements and security baseline
Baseline alignment. Approved gateway and client baselines, connection tests and documented exceptions. CIS IGs · DISA STIGs · DISA SRGs
- Approved sites, remote users and required service paths
- Authentication, cryptographic policy and least-privilege access
- Gateway or client versions, logging and recovery requirements
Deployment and control mapping
Site-to-site and remote-access VPN Deployment and control mapping
- Scope and ownership: Site-to-site and remote-access VPN services, with the gateway, client and access requirements documented for each deployment.
- Approved rollout and acceptance: Pilot site-to-site or remote-access configuration; authentication, intended service and prohibited-path tests
- Applicable requirements mapped to configuration, validation evidence and approved exceptions
Client and user guide
Site-to-site and remote-access VPN Client and user guide
- Using the approved remote-access client and sign-in method
- Reporting connection problems with useful context
- Protecting access credentials and ending a session
Technician training outline
Site-to-site and remote-access VPN Technician training outline
- Tunnel, route, selector and client configuration
- Authentication and allowed or denied traffic investigation
- Authorized changes, rollback and service-path validation
RDA technician workflow
Site-to-site and remote-access VPN RDA technician workflow
- Identify and assess the requirement; plan the scope, accountable owner and required approvals
- Implement and verify: Establish the intended VPN path, verify the required application and confirm that prohibited paths remain denied.
- Document the configuration and result; hand off operation, review exceptions and plan lifecycle changes
Portal and access training
Site-to-site and remote-access VPN Portal and access training
- Named gateway administrators and restricted management access
- Remote-user and service-account lifecycle
- Multifactor requirements, access review and emergency access
Training module template
Site-to-site and remote-access VPN Training module template
- Learning objectives and prerequisites: tunnel, route, selector and client configuration
- Authorized practical exercise: Establish the intended VPN path, verify the required application and confirm that prohibited paths remain denied.
- Knowledge check, observed result and instructor or responsible-owner sign-off
Basic installation and acceptance
Site-to-site and remote-access VPN Basic installation and acceptance
- Selected vendor, supported gateway and client prerequisites
- Pilot site-to-site or remote-access configuration
- Authentication, intended service and prohibited-path tests
Advanced deployment and changes
Site-to-site and remote-access VPN Advanced deployment and changes
- Additional sites, access groups and scoped routing changes
- Resilience or failover options where contracted and supported
- Staged gateway or client updates and rollback
Technical configuration and integrations
Site-to-site and remote-access VPN Technical configuration and integrations
- Vendor-specific topology, routes, selectors and access policies
- Identity dependencies and approved event collection
- Configuration backup, version records and log retention
Operational audit and checklist
Site-to-site and remote-access VPN Operational audit and checklist
- Coverage and operating checks: failed authentication, unstable tunnels and stale clients
- Evidence sample: vendor-specific tunnel, session and traffic-event records; allowed and denied service-path tests with recovery results
- Review date and owner; pass or fail, exceptions, corrective action and retest evidence
Tabletop exercises
Site-to-site and remote-access VPN Tabletop exercises
- The tunnel is up but the required application is unreachable
- A departed user retains remote-access capability
- A gateway change permits an unintended network path
Response playbook
Site-to-site and remote-access VPN Response playbook
- Assess authentication, routing and application impact
- Authorize access repair, containment or configuration rollback
- Retest required and forbidden paths and document the handback
Operational runbooks
Site-to-site and remote-access VPN Operational runbooks
- Collect vendor-specific tunnel and session diagnostics
- Repair an approved VPN configuration and test service access
- Remove remote access and verify that reconnect is denied
Evaluation and lifecycle review
Site-to-site and remote-access VPN Evaluation and lifecycle review
Selection and fit. Compare viable options against the business need, security requirements, existing systems and full operating cost. Record the reasons for the selection, the tradeoffs accepted and the conditions that would prompt a different choice.
Keeping the choice current. Follow supplier notices between scheduled reviews and reassess before renewal or a material change. Check ownership changes, renamed or retired products, subscription and licensing terms, pricing, capabilities and support commitments. Record the effect on security, data handling, integrations and service continuity. Assign an owner to approve adjustments or plan a transition, including data export and removal of access.
- Selected vendor, product, support and license scope
- Required-service access and denied-path validation
- Recovery behavior, client maintenance and total cost