
“It is encrypted” leaves several questions unanswered. A laptop disk, an email connection, a shared file, and a cloud database may each use encryption differently. Start with the information and the situation the protection must address: a lost device, an intercepted connection, an exposed export, or access by a service provider.
Where does encryption protect the information?
Identify the protected boundary before relying on the word encrypted.
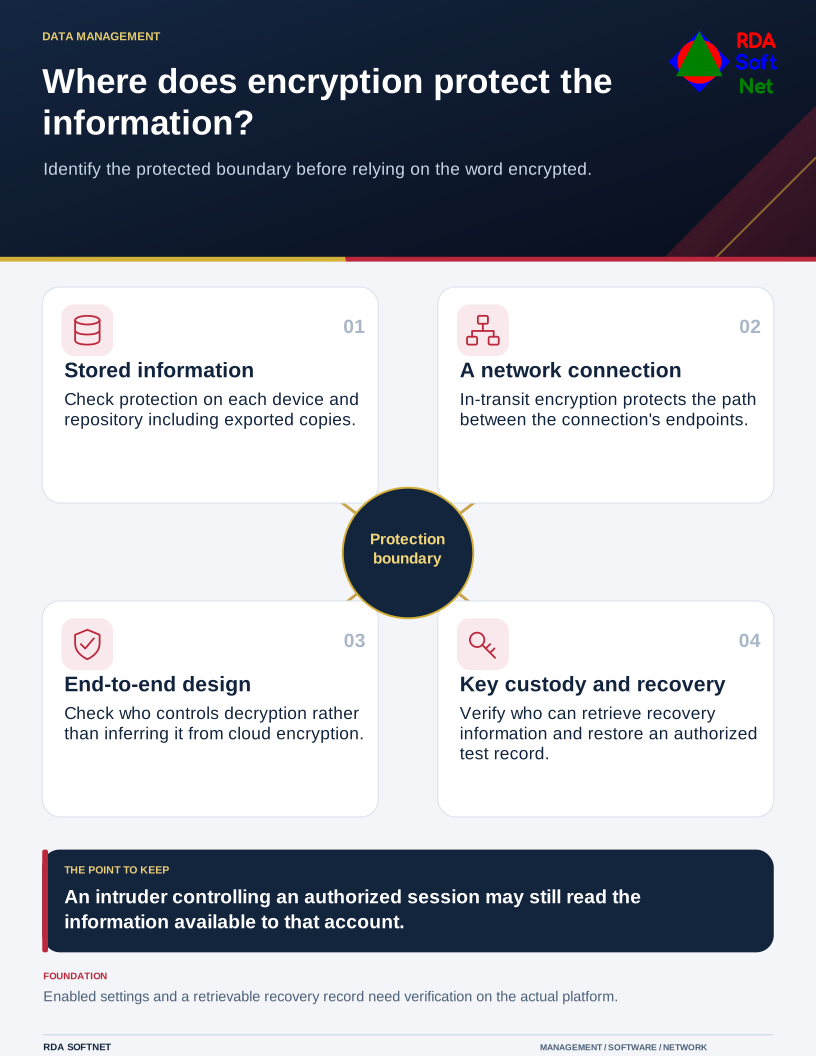
Encryption at rest protects stored information under the conditions of the particular implementation. Encryption in transit protects a connection between its endpoints. End-to-end encryption is a more specific design in which the communicating endpoints control decryption; do not assume a cloud service offers it because the service also encrypts disks and network traffic.
Check the configuration and the recovery path
For each important data location, record the responsible administrator, enabled protection, key custody, and recovery arrangement. Include removable media, exports, backups, and copies created by integrations. An encrypted production database does not tell you how an exported spreadsheet is protected.
Microsoft's BitLocker recovery process illustrates the operating responsibility: recovery information must be retrievable securely, and backup to an organizational directory requires the appropriate configuration. Check the actual recovery record rather than assuming enrollment completed it. Restrict who can release recovery information and verify the requester's identity.
Keep protection connected to access
An authorized application normally needs readable information to do its work. Encryption alone will not stop an intruder who controls an authorized session from using that access. Maintain permissions and information-handling rules, supported devices, and a response process alongside encryption.
Include keys and necessary identities in a controlled recovery exercise. Confirm that an authorized person can restore an appropriate test record when the original device or primary administrator is unavailable. Keep the test evidence without exposing the recovery secrets in the ordinary support record.